CVE Watch
Recently disclosed vulnerabilities, checked against the vendor advisory and the CVE record.
CVE Watch
- CVE-2024-27834Apple iOS, iPadOS, macOS, Safari, tvOS, watchOSCVE published: CVSS 3.1: 5.5, scored by CISA ADPExploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-119977WordPress CoreCVE published: CVSS 3.1: 8.1, scored by Wordfence (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-118527Ivanti Connect SecureCVE published: CVSS 3.1: 4.3, scored by Ivanti (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-121126Google Chrome (Core)CVE published: CVSS 3.1: 9.6, scored by CISA ADPNo public reports of exploitation
- CVE-2026-121203Google Chrome (Geometry)CVE published: CVSS 3.1: 8.8, scored by CISA ADPNo public reports of exploitation
- CVE-2026-121247Google Chrome for Android (Dawn)CVE published: CVSS 3.1: 9.6, scored by CISA ADPNo public reports of exploitation
- CVE-2026-121035Google Chrome (Prerender)CVE published: CVSS 3.1: 9.6, scored by CISA ADPNo public reports of exploitation
- CVE-2026-121246Google Chrome for Android (WebGL)CVE published: CVSS 3.1: 9.6, scored by CISA ADPNo public reports of exploitation
- CVE-2026-121229Google Chrome for Android (ANGLE)CVE published: CVSS 3.1: 9.6, scored by CISA ADPNo public reports of exploitation
- CVE-2026-121156Google Chrome (Dawn)CVE published: CVSS 3.1: 9.6, scored by CISA ADPNo public reports of exploitation
- CVE-2026-58936Android System (libpng)CVE published: CVSS 3.1: 9.8, scored by CISA ADPNo public reports of exploitation
- CVE-2026-58876Android SystemCVE published: CVSS 3.1: 9.8, scored by CISA ADPNo public reports of exploitation
- CVE-2026-58868Android FrameworkCVE published: CVSS 3.1: 9.8, scored by CISA ADPNo public reports of exploitation
- CVE-2026-111357Ivanti Connect SecureCVE published: CVSS 3.1: 7.0, scored by MITRE (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-76418Cisco Secure Firewall ASA / FTDCVE published: CVSS 3.1: 8.6, scored by Cisco (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-97229GitLab CE/EECVE published: CVSS 3.1: 10.0, scored by GitLab (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-41709VMware ESXCVE published: CVSS 3.1: 2.7, scored by VMware (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-46300Linux kernelCVE published: CVSS 3.1: 7.8, scored by Linux kernel CNAExploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-111497Google BrotliCVE published: CVSS 4.0: 9.2, scored by Google (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-48356Adobe Commerce / Magento Open SourceCVE published: CVSS 3.1: 9.3, scored by Adobe (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-109619PHPCVE published: CVSS 4.0: 9.2, scored by PHP Group (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-109618PHPCVE published: CVSS 4.0: 9.2, scored by PHP Group (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-104935Ivanti Connect SecureCVE published: CVSS 3.1: 8.6, scored by Ivanti (CNA)Exploited in real attacks (confirmed)Added to CISA KEV:
- CVE-2026-58115Siemens SIMATIC IoT2050 (Node-RED)CVE published: CVSS 3.1: 10.0, scored by Siemens (CNA)Attack attempts observed; no confirmed compromise yet
CVE-2026-58115: attackers are probing Siemens IoT2050 gateways through Node-RED, but no real device is confirmed hacked
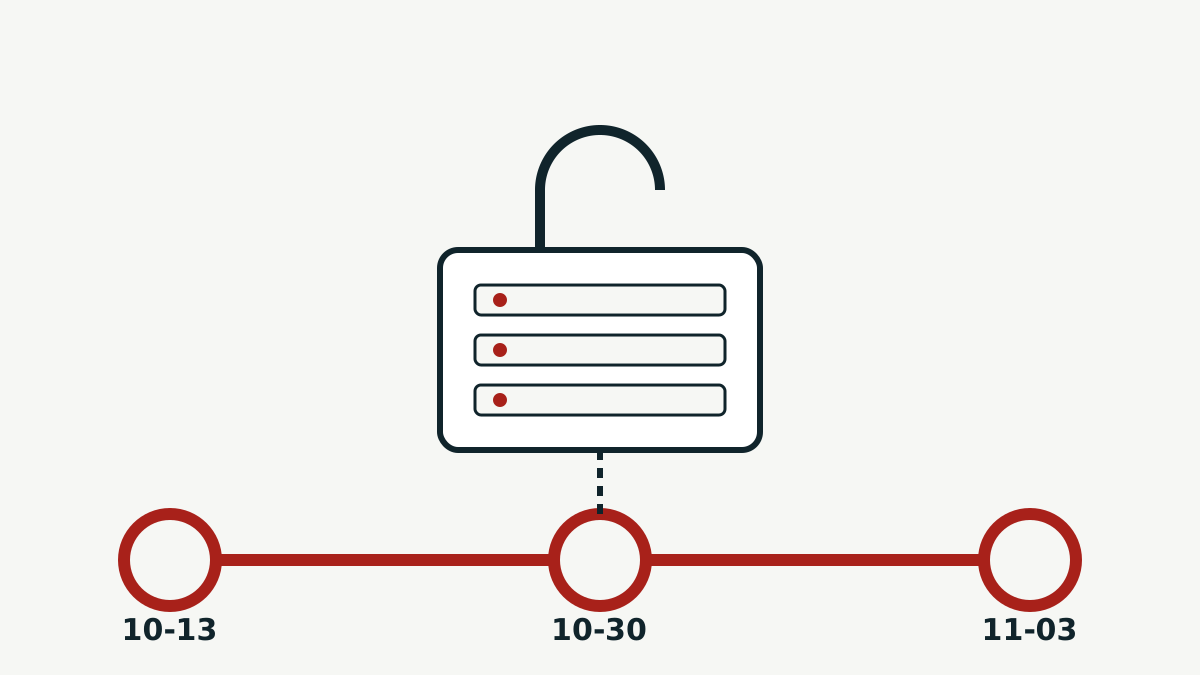
A Siemens advisory rates CVE-2026-58115 at the maximum CVSS score of 10.0. Since October 30, VulnCheck has seen attackers use it against decoy systems to drop a Linux bot and backdoors. Headlines say hackers are backdooring Siemens devices, but no compromise of a real device has been confirmed.
Ivanti Connect Secure: three flaws used in attacks since October, update and check for compromise
CISA says attackers are chaining flaws in Ivanti Connect Secure VPN appliances to run commands without logging in, steal credentials and take data. Two more flaws joined its exploited list on October 30, and one of their CVE records was published on November 3.
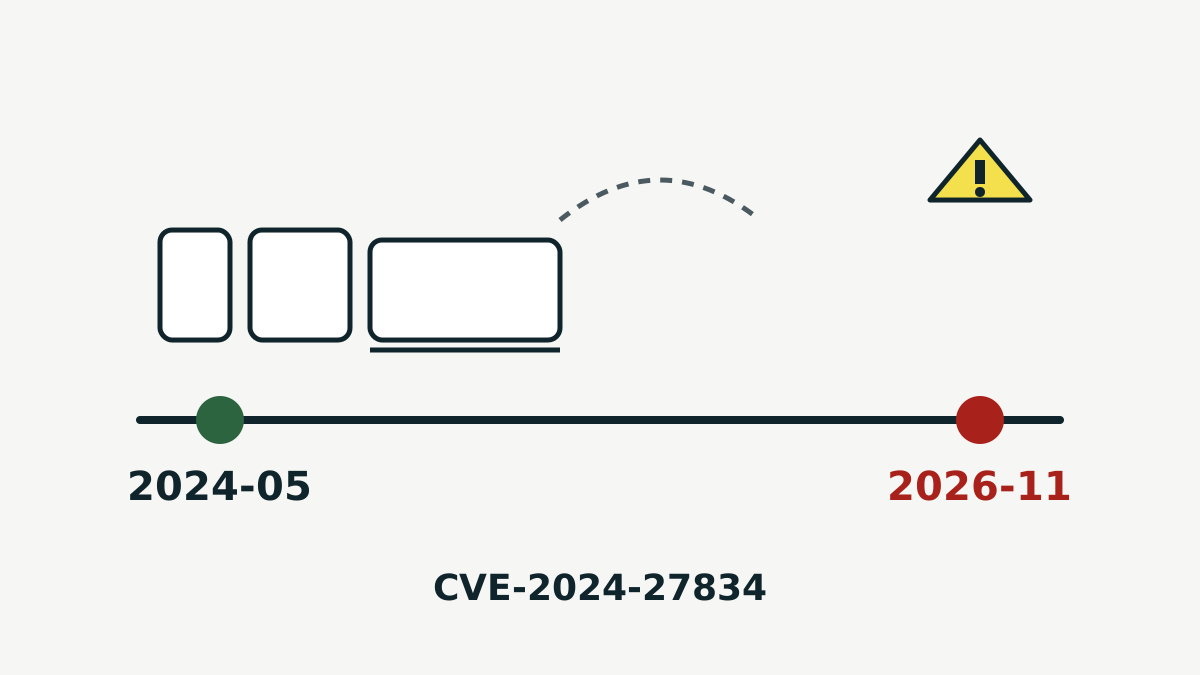
CVE-2024-27834: an Apple flaw fixed in 2024 is now confirmed as exploited
CISA added CVE-2024-27834 to its list of exploited vulnerabilities on November 4, 2026. The bug lets an attacker who can already read and write memory bypass Pointer Authentication. Apple fixed it in May 2024, so updated devices are protected.
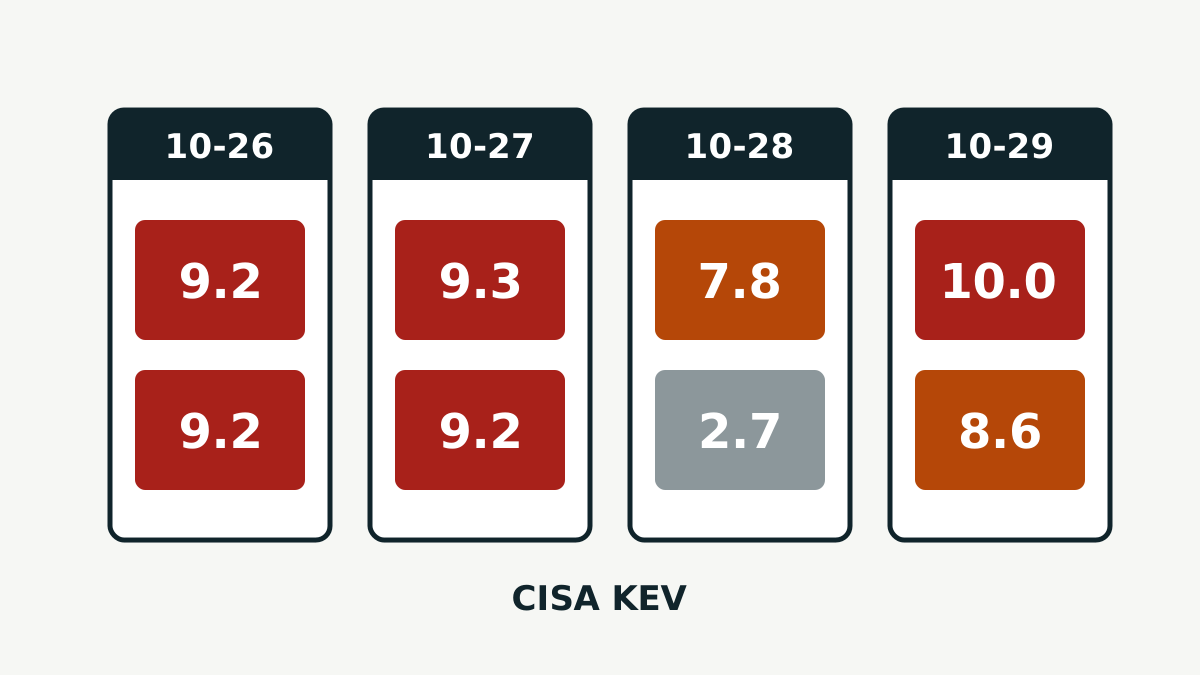
Eight flaws confirmed as exploited in four days: GitLab, Adobe Commerce, PHP, Brotli, Cisco, Linux and VMware
Between October 26 and 29, 2026, CISA added eight vulnerabilities to its list of flaws used in real attacks. They hit code servers, online stores, PHP sites, a compression library, Cisco firewalls, the Linux kernel and VMware hosts. Here is what each one affects and what to install.
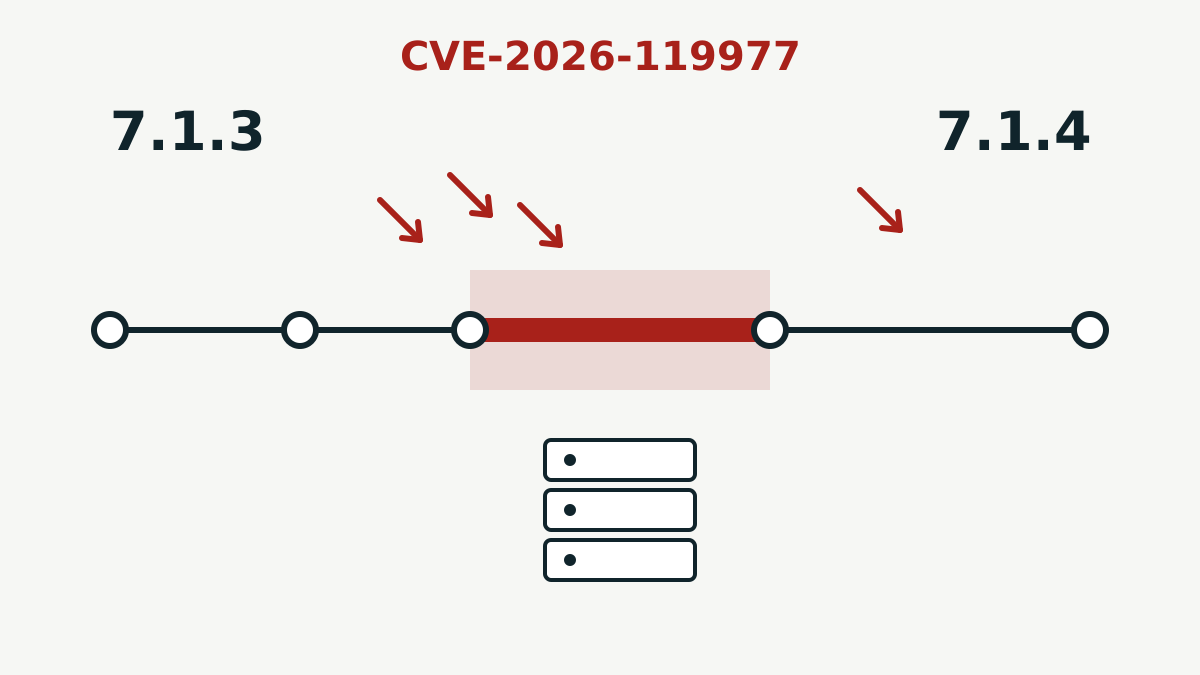
CVE-2026-119977: WordPress upgrade flaw is being exploited, update to 7.1.4
A race condition in the WordPress Core updater lets an unauthenticated attacker run code on the server while an upgrade is in progress. CISA confirmed active exploitation on November 3. WordPress 7.1.4 fixes it.