All news
Every article we have published, newest first.
CVE-2026-58115: attackers are probing Siemens IoT2050 gateways through Node-RED, but no real device is confirmed hacked
A Siemens advisory rates CVE-2026-58115 at the maximum CVSS score of 10.0. Since October 30, VulnCheck has seen attackers use it against decoy systems to drop a Linux bot and backdoors. Headlines say hackers are backdooring Siemens devices, but no compromise of a real device has been confirmed.
The first touchscreen Mac goes on sale: what the MacBook Pro with PROLED XDR display changes
Apple's MacBook Pro with a tandem OLED touch display and M5 Pro or M5 Max chips goes on sale on November 6. It is the first Mac with a touchscreen and brings the Dynamic Island to macOS. Prices start at $2,899 in the US.
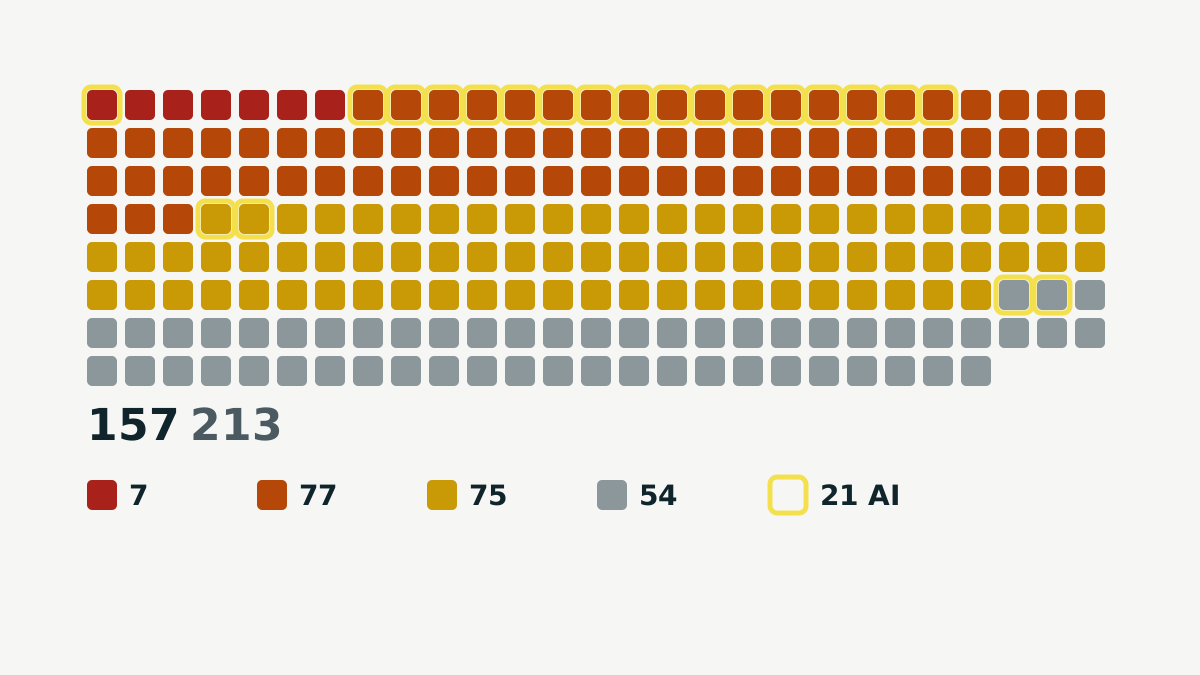
Chrome 157 fixes 213 security flaws, and 21 were found with help from AI tools
Google moved Chrome 157 to the stable channel on November 3 with 213 security fixes, seven of them critical. None is reported as exploited. Twenty-one of the flaws were credited to researchers working with Claude or to OpenAI's Codex Security.
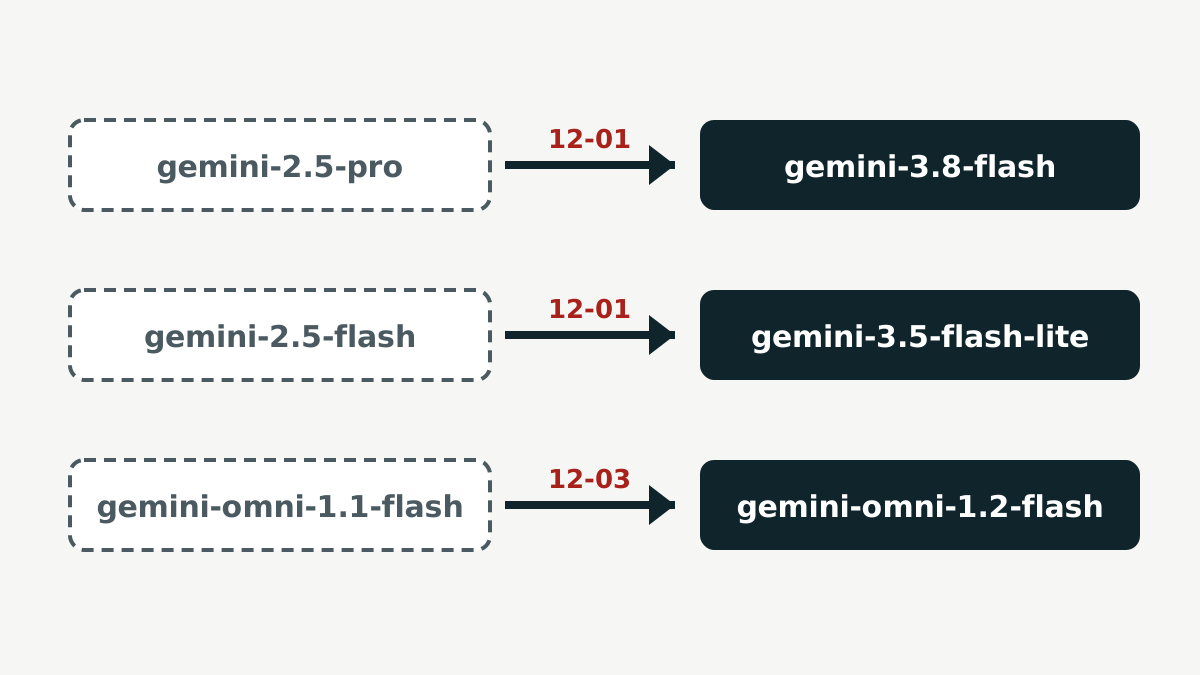
Gemini API: Omni 1.2 Flash goes GA, and Gemini 2.5 Pro and Flash will be rerouted on December 1
Google's Gemini API release notes for early November bring a generally available video model, Gemini Omni 1.2 Flash, and the retirement of Gemini 2.5 Pro and 2.5 Flash. From December 1, requests to the old names go to newer models, with breaking changes. New paid projects also store requests by default.
Ivanti Connect Secure: three flaws used in attacks since October, update and check for compromise
CISA says attackers are chaining flaws in Ivanti Connect Secure VPN appliances to run commands without logging in, steal credentials and take data. Two more flaws joined its exploited list on October 30, and one of their CVE records was published on November 3.
CVE-2024-27834: an Apple flaw fixed in 2024 is now confirmed as exploited
CISA added CVE-2024-27834 to its list of exploited vulnerabilities on November 4, 2026. The bug lets an attacker who can already read and write memory bypass Pointer Authentication. Apple fixed it in May 2024, so updated devices are protected.
Eight flaws confirmed as exploited in four days: GitLab, Adobe Commerce, PHP, Brotli, Cisco, Linux and VMware
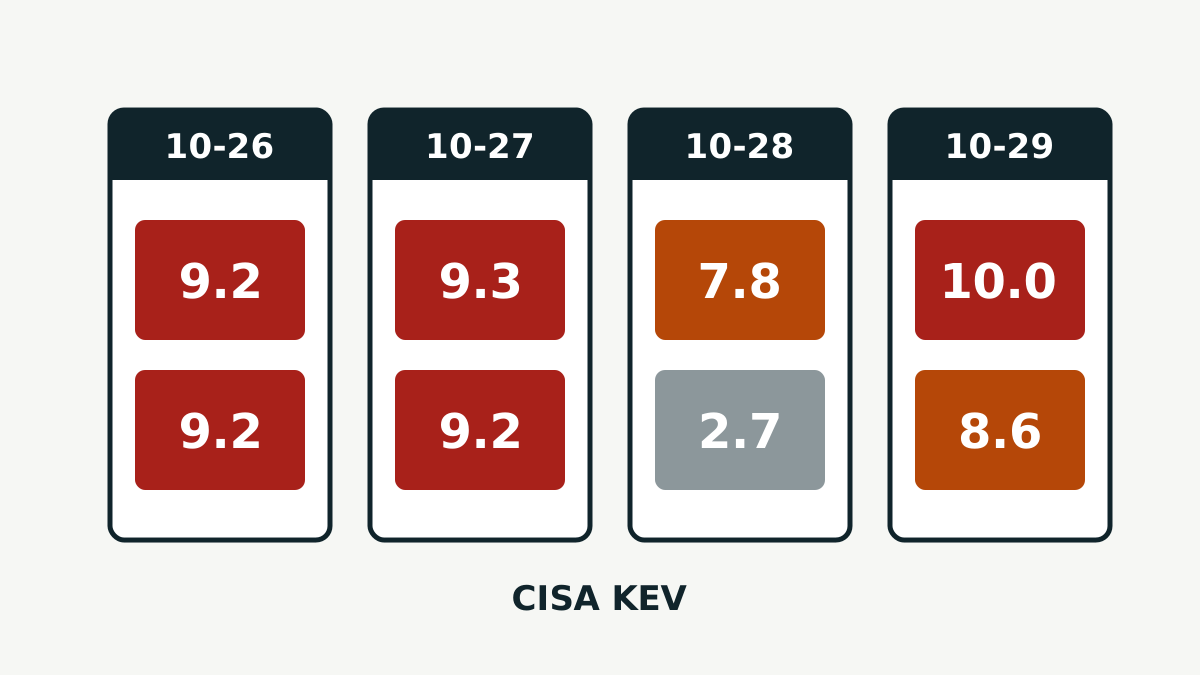
Between October 26 and 29, 2026, CISA added eight vulnerabilities to its list of flaws used in real attacks. They hit code servers, online stores, PHP sites, a compression library, Cisco firewalls, the Linux kernel and VMware hosts. Here is what each one affects and what to install.
Android November 2026 security update fixes 216 flaws, including a critical Framework bug
Google's November bulletin covers Android 14 through 17. The worst bug, CVE-2026-58868, could let an attacker run code on a phone without any tap from the owner. Google has not reported any of the flaws as exploited.
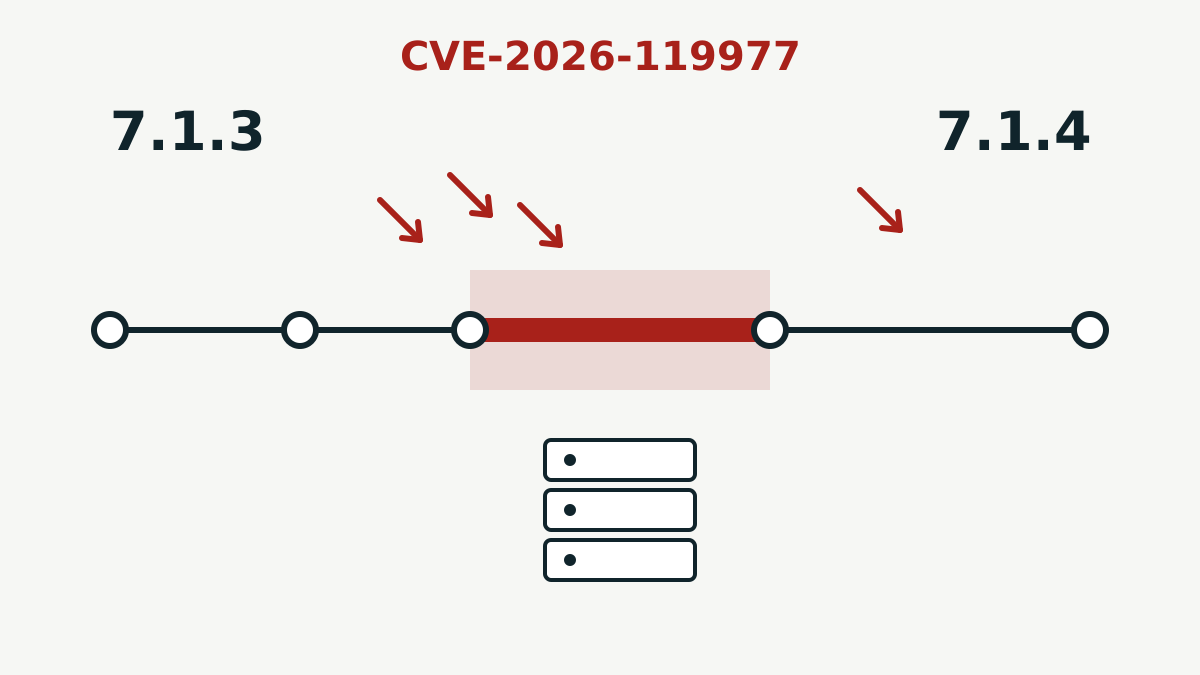
CVE-2026-119977: WordPress upgrade flaw is being exploited, update to 7.1.4
A race condition in the WordPress Core updater lets an unauthenticated attacker run code on the server while an upgrade is in progress. CISA confirmed active exploitation on November 3. WordPress 7.1.4 fixes it.
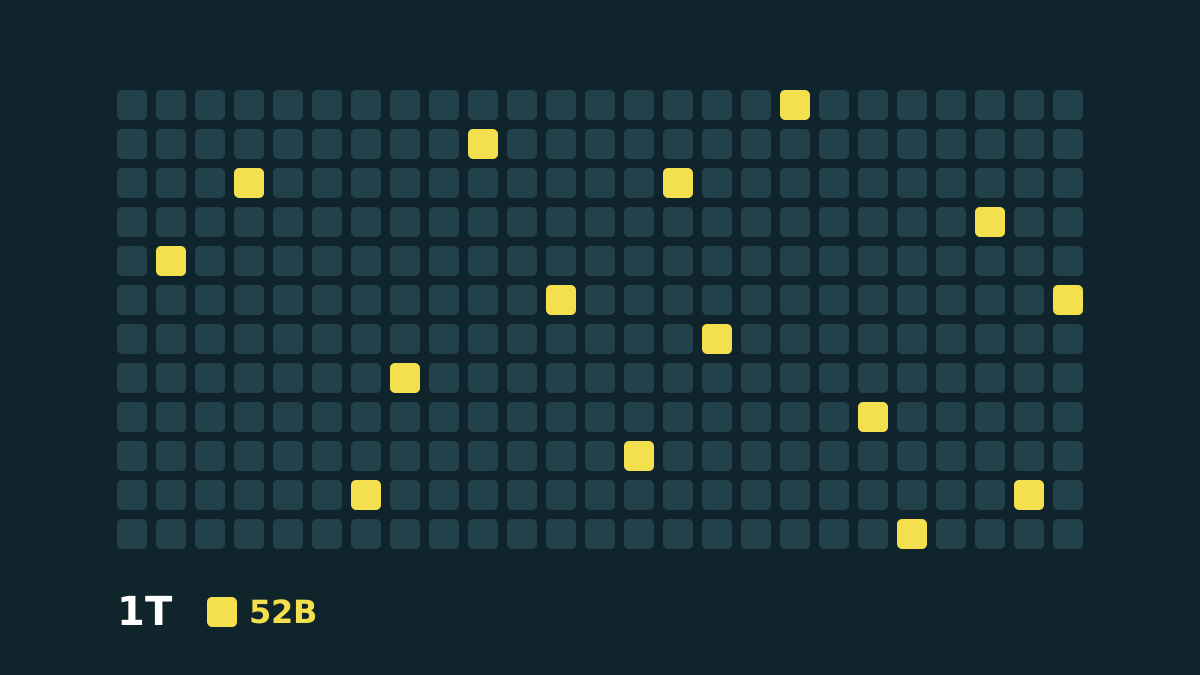
Mistral releases the weights of Mistral Large 4, a 1-trillion-parameter open model
Mistral AI published the weights of its flagship model on October 29 under a modified MIT license. The company highlights coding and cyber-defense results, and also says it sees "a potential for uplift" for real attacks.
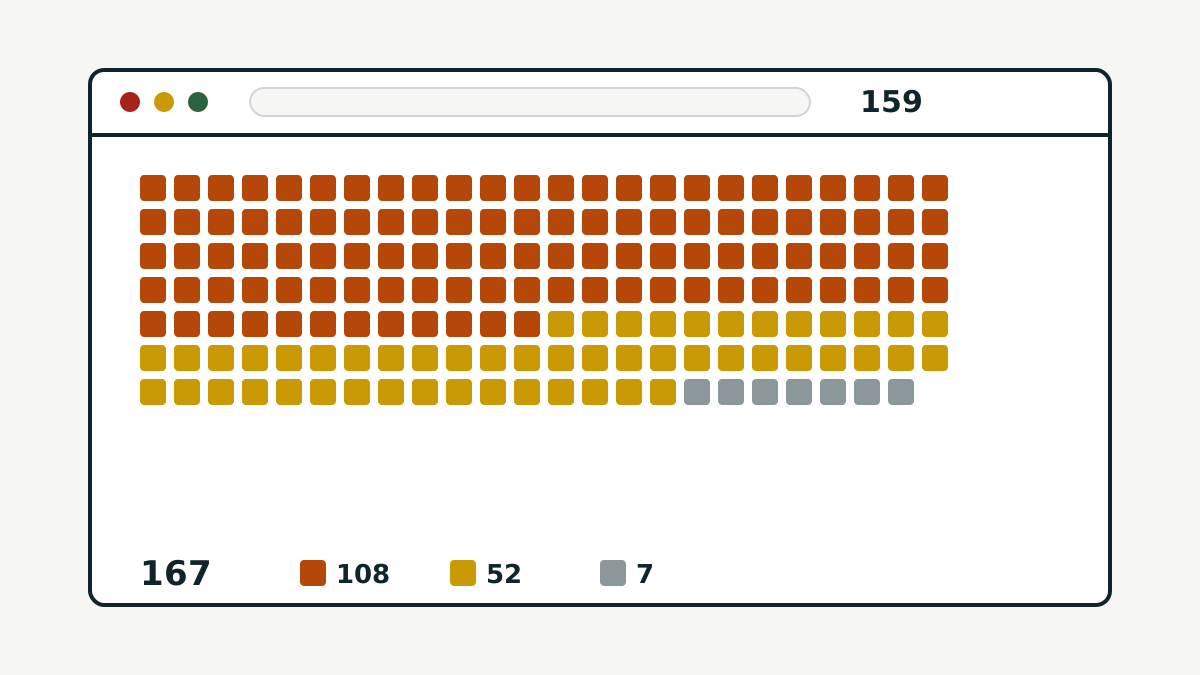
Firefox 159 fixes 167 security vulnerabilities and adds page watching to Smart Window
Mozilla released Firefox 159 on October 27 with fixes for 167 vulnerabilities, 108 of them rated high impact. The update also changes keyboard shortcuts and lets the Smart Window watch pages for price drops.
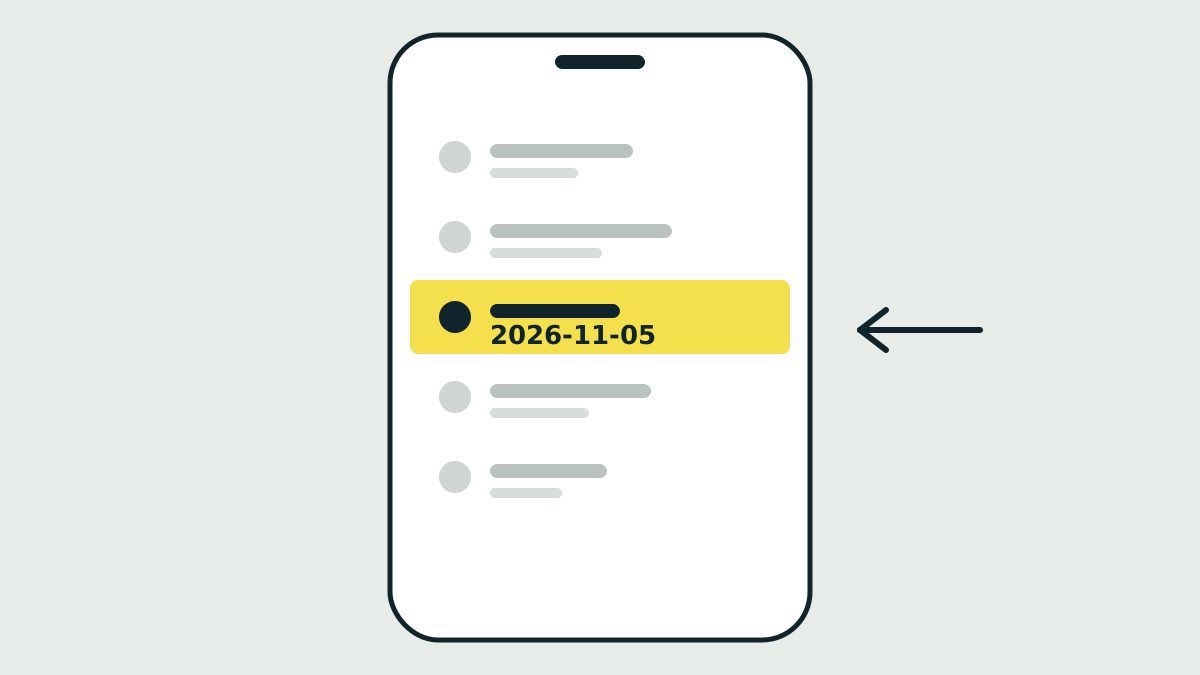
How to check the Android security patch level on your phone
The security patch level is a date in your phone's settings. It tells you which monthly Android security fixes are installed. Here is where to find it, how to read it, and what to do if it is out of date.