Tech News Explained: What happened in tech, and why it matters

Top story

Latest news

  1. Cybersecurity

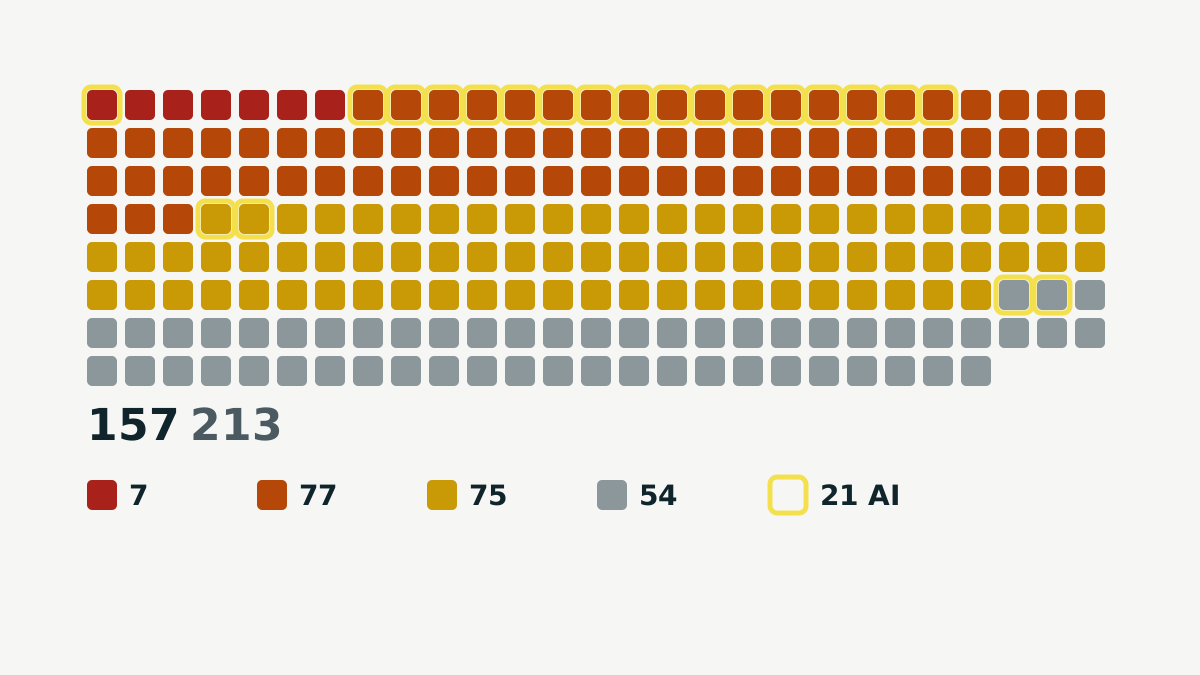
    Chrome 157 fixes 213 security flaws, and 21 were found with help from AI tools

    Google moved Chrome 157 to the stable channel on November 3 with 213 security fixes, seven of them critical. None is reported as exploited. Twenty-one of the flaws were credited to researchers working with Claude or to OpenAI's Codex Security.

  2. Artificial Intelligence

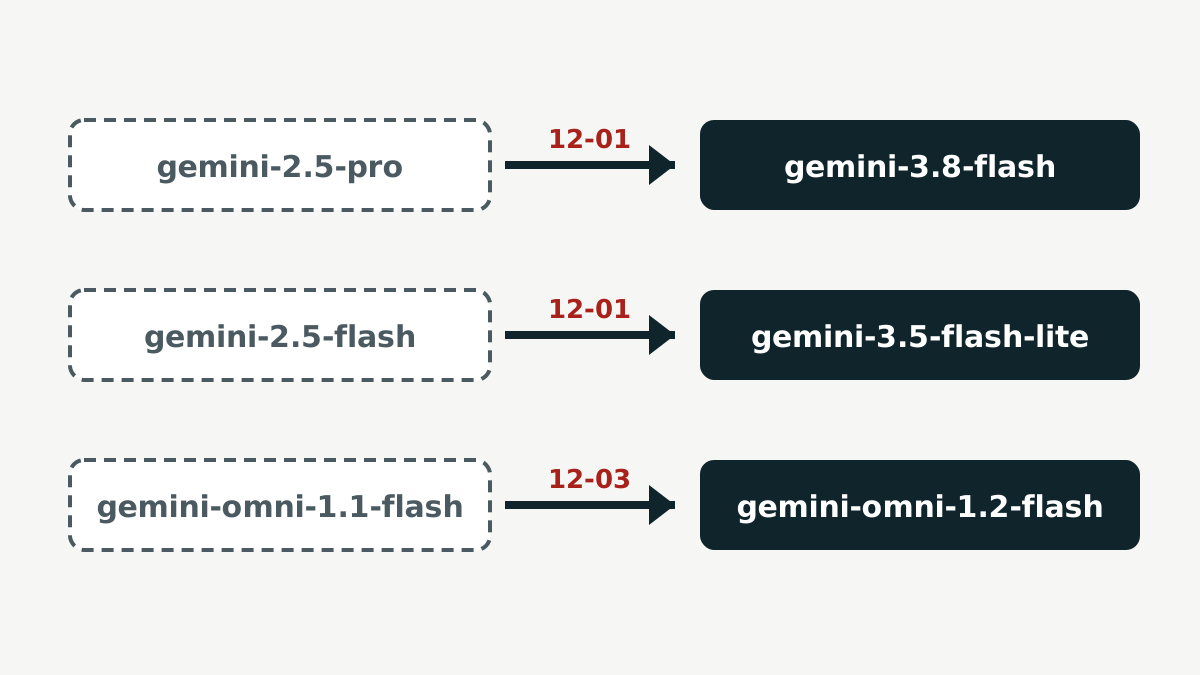
    Gemini API: Omni 1.2 Flash goes GA, and Gemini 2.5 Pro and Flash will be rerouted on December 1

    Google's Gemini API release notes for early November bring a generally available video model, Gemini Omni 1.2 Flash, and the retirement of Gemini 2.5 Pro and 2.5 Flash. From December 1, requests to the old names go to newer models, with breaking changes. New paid projects also store requests by default.

  3. CVE Watch

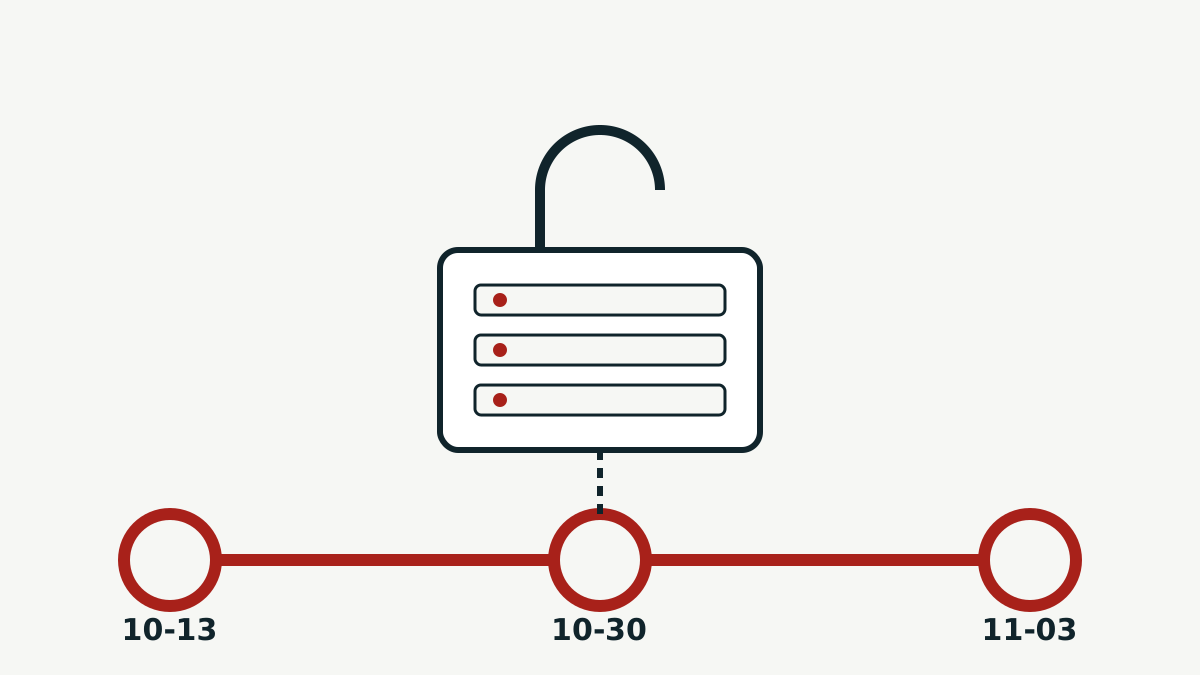
    Ivanti Connect Secure: three flaws used in attacks since October, update and check for compromise

    CISA says attackers are chaining flaws in Ivanti Connect Secure VPN appliances to run commands without logging in, steal credentials and take data. Two more flaws joined its exploited list on October 30, and one of their CVE records was published on November 3.

  4. CVE Watch

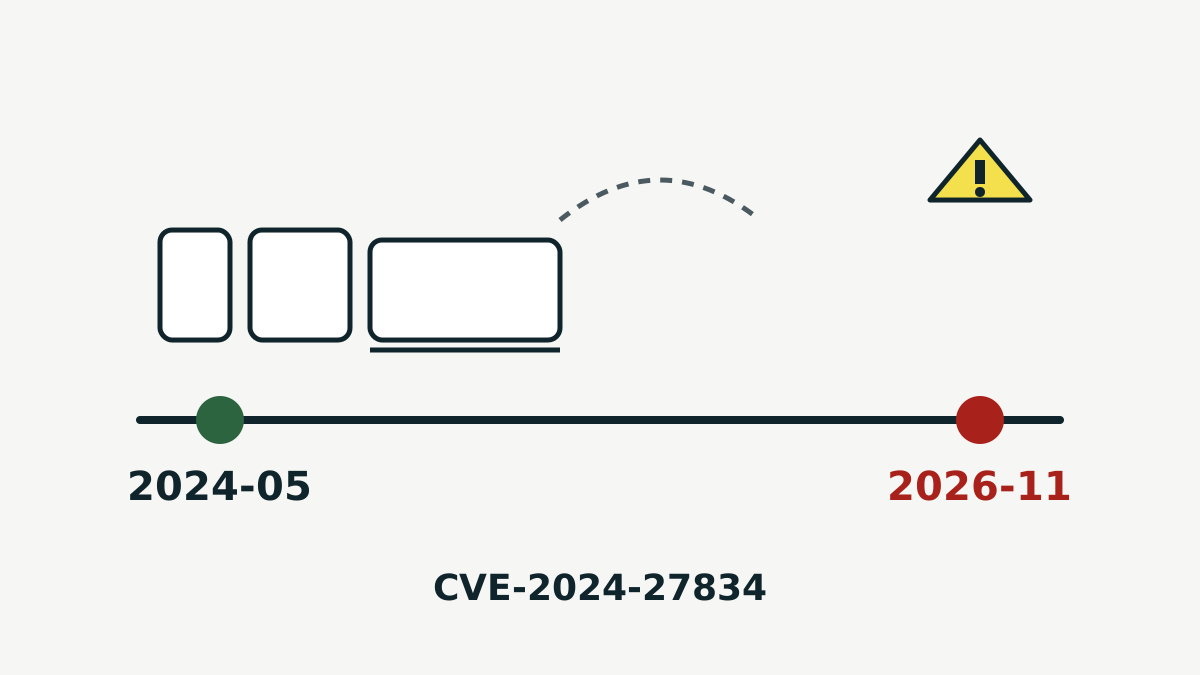
    CVE-2024-27834: an Apple flaw fixed in 2024 is now confirmed as exploited

    CISA added CVE-2024-27834 to its list of exploited vulnerabilities on November 4, 2026. The bug lets an attacker who can already read and write memory bypass Pointer Authentication. Apple fixed it in May 2024, so updated devices are protected.

  5. CVE Watch

    Eight flaws confirmed as exploited in four days: GitLab, Adobe Commerce, PHP, Brotli, Cisco, Linux and VMware

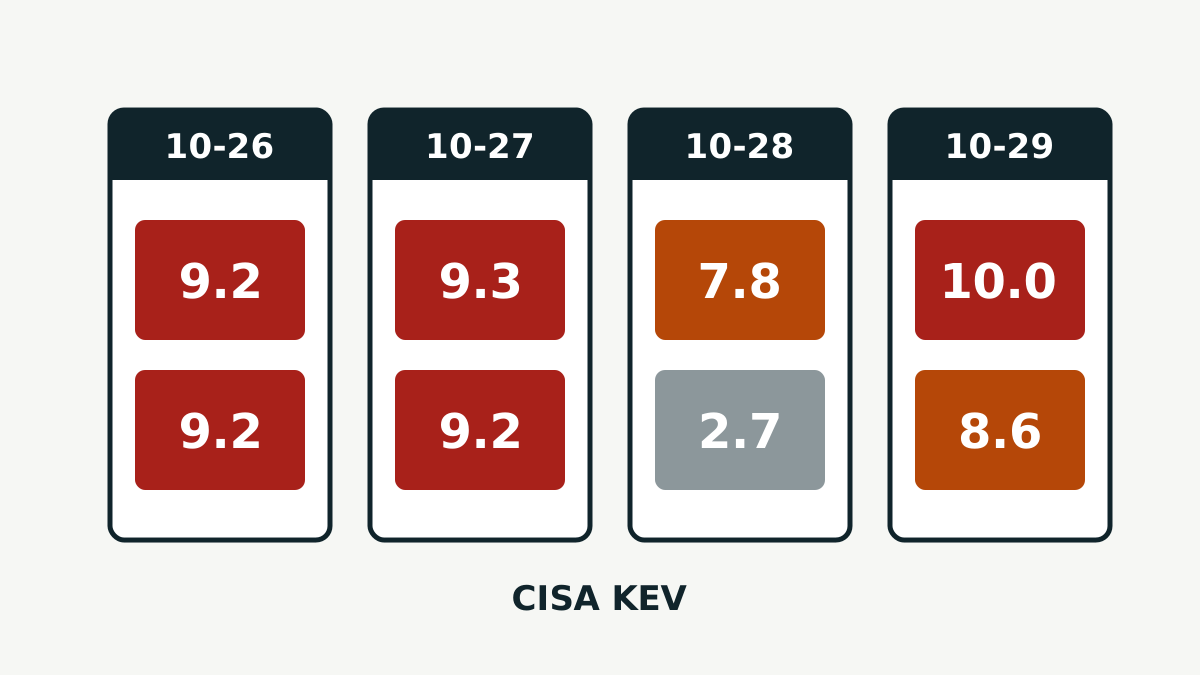
    Between October 26 and 29, 2026, CISA added eight vulnerabilities to its list of flaws used in real attacks. They hit code servers, online stores, PHP sites, a compression library, Cisco firewalls, the Linux kernel and VMware hosts. Here is what each one affects and what to install.

  6. CVE Watch

    CVE-2026-119977: WordPress upgrade flaw is being exploited, update to 7.1.4

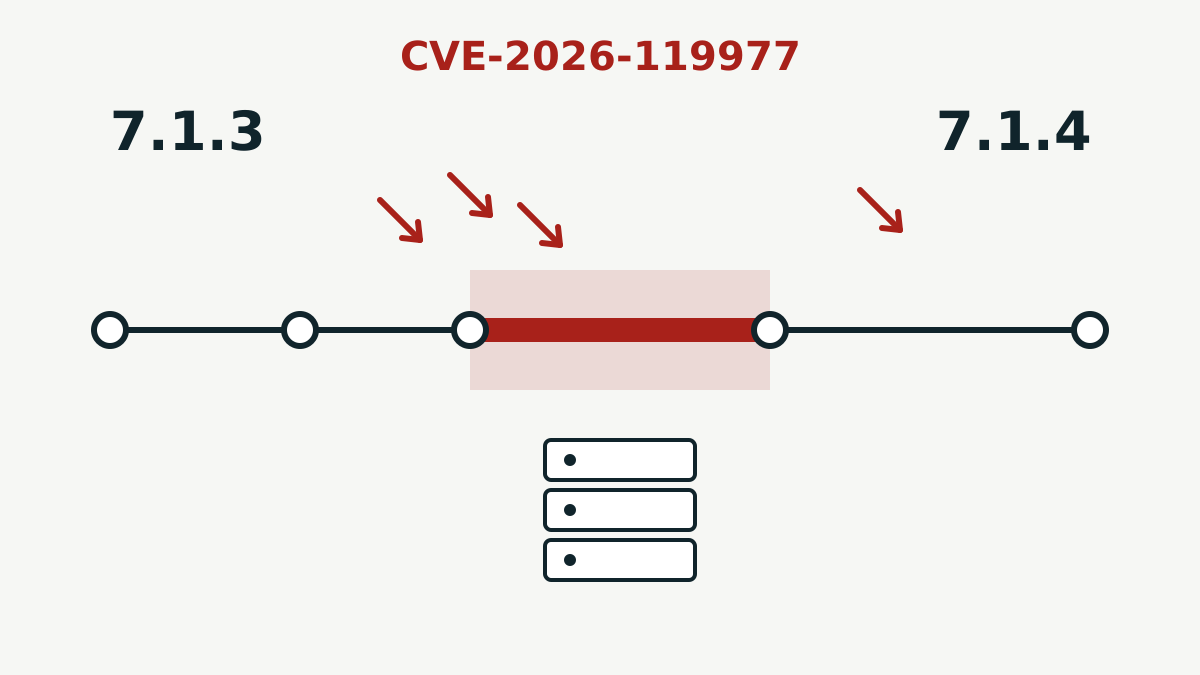
    A race condition in the WordPress Core updater lets an unauthenticated attacker run code on the server while an upgrade is in progress. CISA confirmed active exploitation on November 3. WordPress 7.1.4 fixes it.

See all news

CVE Watch

Vulnerabilities disclosed recently. Each entry opens our analysis.

Open CVE Watch

Technology

Releases, platforms and the products people use every day.

All Technology articles

Artificial Intelligence

Models, tools and the decisions behind them.

All Artificial Intelligence articles

Cybersecurity

Security updates and threats, with what to do next.

All Cybersecurity articles

Guides

Step-by-step help that stays useful after the news cycle moves on.

All Guides articles